Why Does RSA Actually Work?

March 23, 2023 by patrickd
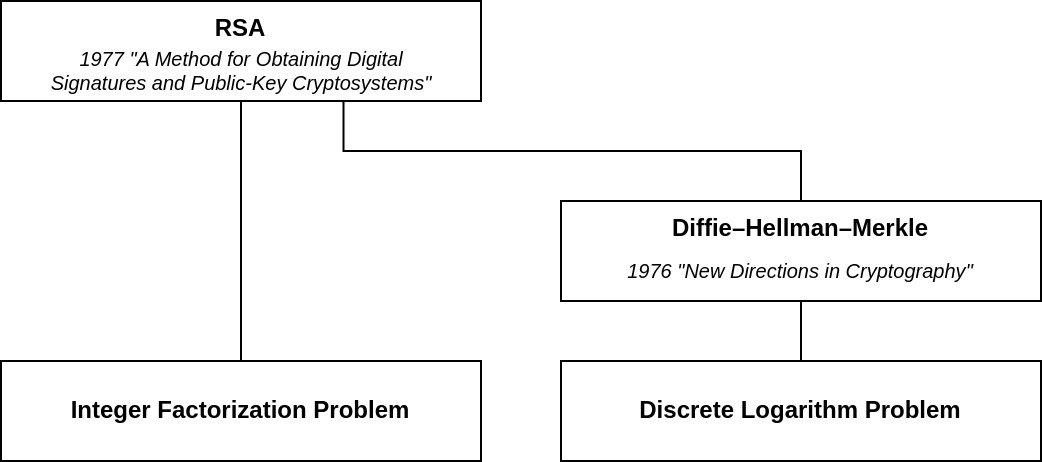
Tech-Tree diagram of RSA

RSA encryption appears so incredibly elegant and simple, it's as if it were some sort of mathematical magic. This article is an attempt to give the reader some intuition about why it works and make the seemingly magical aspects graspable. Note that it avoids mathematical proves where possible, it does not attempt to give an explanation on how to implement RSA securely or efficiently, and it skips any concepts that have been deemed irrelevant for understanding the "why".

The Magic

p{p} and q{q} chosen as large random prime numbers

N=p⋅q{N}={p}\cdot{q}

ϕ(N)=ϕ(p)⋅ϕ(q)=(p−1)⋅(q−1)\phi{\left({N}\right)}=\phi{\left({p}\right)}\cdot\phi{\left({q}\right)}={\left({p}-{1}\right)}\cdot{\left({q}-{1}\right)}, phi being "Euler's Totient Function"

e=65537{e}={65537}, fullfills requirements of 1<e<ϕ(n){1}<{e}<\phi{\left({n}\right)} and gcd⁡(e,ϕ(n))=1{\gcd{{\left({e},\phi{\left({n}\right)}\right)}}}={1}, combined with N{N} makes up the public key K(e,N){K}{\left({e},{N}\right)}

d≡e−1  mod  ϕ(N){d}\equiv{e}^{{-{1}}}\ \text{ mod }\ \phi{\left({N}\right)}, combined with N{N} makes up the private key k(d,N){k}{\left({d},{N}\right)}

c≡me  mod  N{c}\equiv{m}^{{e}}\ \text{ mod }\ {N}, is the encrypted ciphertext c{c} of the message m{m}

m≡cd  mod  N{m}\equiv{c}^{{d}}\ \text{ mod }\ {N}, is the decrypted message m{m} from the ciphertext c{c}


What is ≡mod\equiv\text{mod} ?

You might already know that the triple line equal sign ≡\equiv stands for "congruence" rather than "equality" while mod\text{mod} is short for modulo which yields the remainder of a division operation.

In congruence both sides have the same remainder when divided by a particular modulus.

(a≡b  mod  n)⇔(b≡a  mod  n){\left({a}\equiv{b}\ \text{ mod }\ {n}\right)}\Leftrightarrow{\left({b}\equiv{a}\ \text{ mod }\ {n}\right)}

a  mod  n=b  mod  n{a}\ \text{ mod }\ {n}={b}\ \text{ mod }\ {n}

Example

(2  mod  5=2){\left({2}\ \text{ mod }\ {5}={2}\right)} and (12  mod  5=2){\left({12}\ \text{ mod }\ {5}={2}\right)}

therefore

(2≡12  mod  5){\left({2}\equiv{12}\ \text{ mod }\ {5}\right)} and (12≡2  mod  5){\left({12}\equiv{2}\ \text{ mod }\ {5}\right)}


What is e−1{e}^{{-{1}}} ?

One might expect this to be e−1=(1e)1{e}^{{-{1}}}={\left(\frac{{1}}{{e}}\right)}^{{1}}, but we're only dealing with integers here and not rationals, so what could it be?

According to RSA the following should be true:

m≡cd  mod  N{m}\equiv{c}^{{d}}\ \text{ mod }\ {N}

m≡(me  mod  N)d  mod  N{m}\equiv{\left({m}^{{e}}\ \text{ mod }\ {N}\right)}^{{d}}\ \text{ mod }\ {N}

m≡me⋅d  mod  N{m}\equiv{m}^{{{e}\cdot{d}}}\ \text{ mod }\ {N}

m≡m1  mod  N{m}\equiv{m}^{{1}}\ \text{ mod }\ {N}

m≡m  mod  N{m}\equiv{m}\ \text{ mod }\ {N}

The public exponent e{e} and the private exponent d{d} are cancelling each other out, making them "inverse" to each other. So in modular arithmetic e−1{e}^{{-{1}}} is the "modular multiplicative inverse" of e{e}.

e⋅d≡e⋅e−1≡1  mod  ϕ(N){e}\cdot{d}\equiv{e}\cdot{e}^{{-{1}}}\equiv{1}\ \text{ mod }\ \phi{\left({N}\right)}

Knowing that, we can also see why the notiation of e−1{e}^{{-{1}}} was chosen to represent the inverse when we go back to using rational numbers:

e⋅d=e⋅e−1=e⋅(1e)1=1{e}\cdot{d}={e}\cdot{e}^{{-{1}}}={e}\cdot{\left(\frac{{1}}{{e}}\right)}^{{1}}={1}


Why does inversion work?

At first it looks quite simple: We just have to find two integers e{e} and d{d} such that when multiplied with each other they result in 1 (within mod  n\text{mod }\ {n}) and are therefore inverse to each other:

e⋅d≡1  mod  n{e}\cdot{d}\equiv{1}\ \text{ mod }\ {n}

An interesting aspect to this is, that it only has solutions when e{e} and d{d} are "coprime" (or "relatively prime") to n{n}. Meaning that the greatest common divisior, the biggest integer that divides both numbers without a remainder, is 1.

gcd⁡(e,n)=1{\gcd{{\left({e},{n}\right)}}}={1} and gcd⁡(d,n)=1{\gcd{{\left({d},{n}\right)}}}={1}

Example

Let's look for the inverse d{d} of 5 within (mod  15){\left(\text{mod }\ {15}\right)}:

5⋅d≡1  mod  15{5}\cdot{d}\equiv{1}\ \text{ mod }\ {15}

With gcd⁡(5,15)=5{\gcd{{\left({5},{15}\right)}}}={5} there should not be a solution for ((d⋅5)  mod  15)=1{\left({\left({d}\cdot{5}\right)}\ \text{ mod }\ {15}\right)}={1}, is that true?

|              d |  0 |  1 |  2 |  3 |  4 |  5 |  6 |   ...    |
|----------------|----|----|----|----|----|----|----|----------|
| ((d⋅5) mod 15) |  0 |  5 | 10 |  0 |  5 | 10 |  0 | {0,5,10} |

The numbers this can yield quickly start to repeat and none of them are 1, so there is indeed no inverse.

Okay, but 15 is a multiple of 5 so the result is not that much of a surprise.

What about 6?

6⋅d≡1  mod  15{6}\cdot{d}\equiv{1}\ \text{ mod }\ {15}

With gcd⁡(6,15)=3{\gcd{{\left({6},{15}\right)}}}={3} there should still not be a solution for ((d⋅6)  mod  15)=1{\left({\left({d}\cdot{6}\right)}\ \text{ mod }\ {15}\right)}={1}, but this time 15 is clearly not a multiple of 6 so what happens now?

|              d |  0 |  1 |  2 |  3 |  4 |  5 |  6 |     ...      |
|----------------|----|----|----|----|----|----|----|--------------|
| ((d⋅6) mod 15) |  0 |  6 | 12 |  3 |  9 |  0 |  6 | {0,3,6,9,12} |

Still no inverse, but something interesting becomes visible: The numbers yielded are always multiples of gcd⁡(e,n){\gcd{{\left({e},{n}\right)}}}.

Let's try a number which should actually have an inverse: gcd⁡(8,15)=1{\gcd{{\left({8},{15}\right)}}}={1}. It may be worth pointing out here that neither numbers are prime, but with this result they are still "relative prime" to each other.

|              d |  0 |  1 |  2 |  3 |  4 |  5 |  6 |  7 |  8 |  9 | 10 | 11 | 12 | 13 | 14 | 15 | 16 | 17 |                ...                   |
|----------------|----|----|----|----|----|----|----|----|----|----|----|----|----|----|----|----|----|----|--------------------------------------|
| ((d⋅8) mod 15) |  0 |  8 |  1 |  9 |  2 | 10 |  3 | 11 |  4 | 12 |  5 | 13 |  6 | 14 |  7 |  0 |  8 |  1 | {0,1,2,3,4,5,6,7,8,9,10,11,12,13,14} |

Not only has 8 an inverse but the numbers yielded are also all numbers from 0 to 14. Thanks to the greatest common divisor being 1, the resulting numbers are multiples of 1 as well. This time it is as if there's a 1-to-1 mapping between d{d} and the resulting numbers as long as d<n{d}\lt{n}.


Why does an inverse from mod  ϕ(N)\text{mod }\ \phi{\left({N}\right)} still seem to work in mod  N\text{mod }\ {N} ?

We've seen that the inverse of an integer depends on the modulo. The inverse for 8 in (mod  15){\left(\text{mod }\ {15}\right)} is 2. But in (mod  13){\left(\text{mod }\ {13}\right)} it would be 5.

In RSA d{d} is calculated as the inverse of e{e} in mod  ϕ(N)\text{mod }\ \phi{\left({N}\right)}:

d≡e−1  mod  ϕ(N){d}\equiv{e}^{{-{1}}}\ \text{ mod }\ \phi{\left({N}\right)} and therefore e⋅d≡1  mod  ϕ(N){e}\cdot{d}\equiv{1}\ \text{ mod }\ \phi{\left({N}\right)}

But during decryption d{d} and e{e} appear to be cancelling each other out even under (mod  N){\left(\text{mod }\ {N}\right)}, why does that work?

m≡me⋅d≡m1  mod  N{m}\equiv{m}^{{{e}\cdot{d}}}\equiv{m}^{{1}}\ \text{ mod }\ {N}

Unfortunately there doesn't seem to be a good way to explain this without making use of (a little bit of magic called) Euler's Totient Theorem which shows that for an integer a{a} that is coprime with n{n} the following applies:

aϕ(n)≡1  mod  n{a}^{{\phi{\left({n}\right)}}}\equiv{1}\ \text{ mod }\ {n}

To make use of that we have to look for a ϕ(N)\phi{\left({N}\right)} in the message's exponent and we can quite easily find it:

e⋅d≡1  mod  ϕ(N)⇒e⋅d=1+k⋅ϕ(N){e}\cdot{d}\equiv{1}\ \text{ mod }\ \phi{\left({N}\right)}\Rightarrow{e}\cdot{d}={1}+{k}\cdot\phi{\left({N}\right)} with the integer k≥0{k}\ge{0}

⇒m≡me⋅d≡m1+k⋅ϕ(N)≡m1⋅mϕ(N)⋅k≡m⋅(mϕ(N))k≡m⋅1k  mod  N\Rightarrow{m}\equiv{m}^{{{e}\cdot{d}}}\equiv{m}^{{{1}+{k}\cdot\phi{\left({N}\right)}}}\equiv{m}^{{1}}\cdot{m}^{{\phi{\left({N}\right)}\cdot{k}}}\equiv{m}\cdot{\left({m}^{{\phi{\left({N}\right)}}}\right)}^{{{k}}}\equiv{m}\cdot{1}^{{k}}\ \text{ mod }\ {N}

Thanks to Euler's Theorem it seems like we can remove everything except for message m{m} from the formula with (mϕ(N)≡1  mod  N){\left({m}^{{\phi{\left({N}\right)}}}\equiv{1}\ \text{ mod }\ {N}\right)}.

But you might remember I mentioned the Theorem should only apply when m{m} is coprime with N{N}, which would restrict the valid messages we would be able to encrypt. If N{N} was a prime that would not be an issue as all integers (1≤m<N){\left({1}\le{m}\lt{N}\right)} would be relatively prime to it.


Why does Euler's Theorem still seem to apply for gcd⁡(m,N)≠1{\gcd{{\left({m},{N}\right)}}}\ne{1}?

First, note that because both p{p} and q{q} are prime their greatest common divisor is always 1. If m{m} is not coprime with N{N} that must mean that it is a multiple of either p{p} or q{q}, meaning it can't be coprime with one of them. But it must be coprime with at least one of them, because in order to not be coprime with both of them it must be a multiple of both p{p} and q{q} and that cannot be the case as long as m<N{m}\lt{N} since N{N} is the first possible number to be a multiple of both: N=p⋅q{N}={p}\cdot{q}.

Therefore even when gcd⁡(m,N)≠1{\gcd{{\left({m},{N}\right)}}}\ne{1} either p{p} or q{q} will share a residue of 0 with the message (since m{m} would be a multiple of it without leaving a remainder) and the other one would be either:

(gdc(m,p)=1)⇒(m⋅mϕ(N)≡m⋅mϕ(p)⋅ϕ(q)≡m⋅(mϕ(p))ϕ(q)≡m⋅1ϕ(q)≡m⋅1  mod  p){\left({g}{d}{c}{\left({m},{p}\right)}={1}\right)}\Rightarrow{\left({m}\cdot{m}^{{\phi{\left({N}\right)}}}\equiv{m}\cdot{m}^{{\phi{\left({p}\right)}\cdot\phi{\left({q}\right)}}}\equiv{m}\cdot{\left({m}^{{\phi{\left({p}\right)}}}\right)}^{{\phi{\left({q}\right)}}}\equiv{m}\cdot{1}^{{\phi{\left({q}\right)}}}\equiv{m}\cdot{1}\ \text{ mod }\ {p}\right)}

or

(gdc(m,q)=1)⇒(m⋅mϕ(N)≡m⋅mϕ(p)⋅ϕ(q)≡m⋅(mϕ(q))ϕ(p)≡m⋅1ϕ(p)≡m⋅1  mod  q){\left({g}{d}{c}{\left({m},{q}\right)}={1}\right)}\Rightarrow{\left({m}\cdot{m}^{{\phi{\left({N}\right)}}}\equiv{m}\cdot{m}^{{\phi{\left({p}\right)}\cdot\phi{\left({q}\right)}}}\equiv{m}\cdot{\left({m}^{{\phi{\left({q}\right)}}}\right)}^{{\phi{\left({p}\right)}}}\equiv{m}\cdot{1}^{{\phi{\left({p}\right)}}}\equiv{m}\cdot{1}\ \text{ mod }\ {q}\right)}

With these, we have either one of the following systems of congruence:

(m≡m  mod  p){\left({m}\equiv{m}\ \text{ mod }\ {p}\right)}, (m≡0  mod  q){\left({m}\equiv{0}\ \text{ mod }\ {q}\right)}

or

(m≡0  mod  p){\left({m}\equiv{0}\ \text{ mod }\ {p}\right)}, (m≡m  mod  q){\left({m}\equiv{m}\ \text{ mod }\ {q}\right)}

Both of which can be simplified using the Chinese Remainder Theorem to:

(m≡m  mod  p⋅q){\left({m}\equiv{m}\ \text{ mod }\ {p}\cdot{q}\right)}

Example

p=7,q=11{p}={7},{q}={11}

N=p⋅q =7⋅11=77{N}={p}\cdot{q}\ ={7}\cdot{11}={77}

ϕ(N)=ϕ(p)⋅ϕ(q)=(p−1)⋅(q−1)=(7−1)⋅(11−1)=60\phi{\left({N}\right)}=\phi{\left({p}\right)}\cdot\phi{\left({q}\right)}={\left({p}-{1}\right)}\cdot{\left({q}-{1}\right)}={\left({7}-{1}\right)}\cdot{\left({11}-{1}\right)}={60}

e=7{e}={7}

d≡e−1  mod  ϕ(N)=43  mod  60{d}\equiv{e}^{{-{1}}}\ \text{ mod }\ \phi{\left({N}\right)}={43}\ \text{ mod }\ {60} with 7⋅43≡1  mod  60{7}\cdot{43}\equiv{1}\ \text{ mod }\ {60}

c≡me  mod  N≡427  mod  77=70{c}\equiv{m}^{{e}}\ \text{ mod }\ {N}\equiv{42}^{{7}}\ \text{ mod }\ {77}={70} with gcd⁡(m,N)=gcd⁡(42,60)=6{\gcd{{\left({m},{N}\right)}}}={\gcd{{\left({42},{60}\right)}}}={6}

m≡cd  mod  N≡7043  mod  77≡42{m}\equiv{c}^{{d}}\ \text{ mod }\ {N}\equiv{70}^{{43}}\ \text{ mod }\ {77}\equiv{42}

Despite m{m} not being coprime with N{N} thanks to:

gcd⁡(m,p)=gcd⁡(42,7)=7{\gcd{{\left({m},{p}\right)}}}={\gcd{{\left({42},{7}\right)}}}={7} therefore m≡m  mod  p≡42  mod  7≡0  mod  7{m}\equiv{m}\ \text{ mod }\ {p}\equiv{42}\ \text{ mod }\ {7}\equiv{0}\ \text{ mod }\ {7}

gcd⁡(m,q)=gcd⁡(42,11)=1{\gcd{{\left({m},{q}\right)}}}={\gcd{{\left({42},{11}\right)}}}={1} therefore m≡med≡m1+k⋅ϕ(q)≡m1⋅(mϕ(q))k≡m⋅1k  mod  q≡42  mod  11{m}\equiv{m}^{{{e}{d}}}\equiv{m}^{{{1}+{k}\cdot\phi{\left({q}\right)}}}\equiv{m}^{{1}}\cdot{\left({m}^{{\phi{\left({q}\right)}}}\right)}^{{k}}\equiv{m}\cdot{1}^{{k}}\ \text{ mod }\ {q}\equiv{42}\ \text{ mod }\ {11}

Therefore m≡m  mod  p⋅q≡42  mod  (7⋅11){m}\equiv{m}\ \text{ mod }\ {p}\cdot{q}\equiv{42}\ \text{ mod }\ {\left({7}\cdot{11}\right)}


Why does Euler's Theorem work?

First of all, Euler's Totient Theorem is a generalization of Fermat's Little Theorem where for a prime p{p} for any integer a{a} the following is true:

(ap≡a  mod  p)⇔(ap−a≡0  mod  p){\left({a}^{{p}}\equiv{a}\ \text{ mod }\ {p}\right)}\Leftrightarrow{\left({a}^{{p}}-{a}\equiv{0}\ \text{ mod }\ {p}\right)}

Next, we need to look at Euler's function, denoted as ϕ(n)\phi{\left({n}\right)}. This function counts the number of positive integers up to n{n} that are relatively prime to n{n}. In other words, it counts the number of integers that have a greatest common divisor of 1 with n{n}. When n{n} is a prime number p{p}, all the numbers from 1{1} to (p−1){\left({p}-{1}\right)} are relatively prime to p{p}, so ϕ(p)=p−1\phi{\left({p}\right)}={p}-{1}.

Euler's Theorem generalizes Fermat's Little Theorem and states that for any positive integer n{n} and any integer a{a} relatively prime to n{n}, we have:

(aϕ(n))≡1(mod  n){\left({a}^{\phi}{\left({n}\right)}\right)}\equiv{1}{\left(\text{mod }\ {n}\right)}

Which is in case for n=p{n}={p} prime equivalent to:

(ap−1)≡1(mod  p){\left({a}^{{{p}-{1}}}\right)}\equiv{1}{\left(\text{mod }\ {p}\right)}

Example

A very simple way to gain some intution for these Theorems is through, what one might call, a modulo-lookup-table:

|    0 |    1 |    2 |    3 |    4 |
|------|------|------|------|------|
|    5 |    6 |    7 |    8 |    9 |
|   10 |   11 |   12 |   13 |   14 |
|   15 |   16 |   17 |   18 |   19 |
|   20 |   21 |   22 |   23 |   24 |
|   25 |   26 |   27 |   28 |   29 |
|   30 |   31 |   32 |   33 |   34 |
:      :      :      :      :      :
|   80 |   81 |   82 |   83 |   84 |
:      :      :      :      :      :
|  240 |  241 |  242 |  243 |  244 |
|  245 |  246 |  247 |  248 |  249 |
|  250 |  251 |  252 |  253 |  254 |
|  255 |  256 |  257 |  258 |  259 |
:      :      :      :      :      :
| 1020 | 1021 | 1022 | 1023 | 1024 |
:      :      :      :      :      :

Imagine this (modulo 5) lookup-table just continues to infinity and always tells us at what remainder we would end up with if we applied (mod5){\left(\text{mod}{5}\right)}.

Now let's check (ap≡a  mod  p){\left({a}^{{p}}\equiv{a}\ \text{ mod }\ {p}\right)}:

0**5 mod 5 =    0 mod 5
1**5 mod 5 =    1 mod 5
2**5 mod 5 =   32 mod 5
3**5 mod 5 =  243 mod 5
4**5 mod 5 = 1024 mod 5

With the help of the lookup-table we can easily determine the remainder of the division by checking in which column we find the number. The Theorem works.

Although it's mathematically equivalent, let's check (ap−a≡0  mod  p){\left({a}^{{p}}-{a}\equiv{0}\ \text{ mod }\ {p}\right)} too:

0**5 mod 5 = (   0 - 0) mod 5 =    0 mod 5
1**5 mod 5 = (   1 - 1) mod 5 =    0 mod 5
2**5 mod 5 = (  32 - 2) mod 5 =   30 mod 5
3**5 mod 5 = ( 243 - 3) mod 5 =  240 mod 5
4**5 mod 5 = (1024 - 4) mod 5 = 1020 mod 5

Here we can see that we always end up in the 0-column, just as we should.

Finally, let's look at ap−1≡1  mod  p{a}^{{{p}-{1}}}\equiv{1}\ \text{ mod }\ {p}:

0**4 mod 5 =    0 mod 5
1**4 mod 5 =    1 mod 5
2**4 mod 5 =   16 mod 5
3**4 mod 5 =   81 mod 5
4**4 mod 5 =  256 mod 5

Since 0 can't have a greatest common divisor with anything, it also can't be coprime so it yields 0 instead of 1. But as long as the base is coprime to the modulo we always end up in the 1-column.


What is the Chinese Remainder Theorem?

The last trick to explain is why the Chinese Remainder Theorem shows that (m≡m⋅mϕ(N)  mod  p⋅q)⇒(m≡m⋅1  mod  p⋅q){\left({m}\equiv{m}\cdot{m}^{{\phi{\left({N}\right)}}}\ \text{ mod }\ {p}\cdot{q}\right)}\Rightarrow{\left({m}\equiv{m}\cdot{1}\ \text{ mod }\ {p}\cdot{q}\right)} despite m{m} not being coprime to both p{p} and q{q}.

The Chinese Remainder Theorem (CRT) allows us to solve a system of linear congruences with pairwise coprime moduli. It states that if you have a system of linear congruences like:

x ≡ a1 (mod n1)
x ≡ a2 (mod n2)
...
x ≡ ak (mod nk)

where n1,n2,…,nk{n}{1},{n}{2},\ldots,{n}{k} are pairwise coprime (i.e., they share no common factors other than 1), then there exists a unique solution for x{x} modulo the product of the moduli, i.e., modulo N=n1⋅n2⋅{N}={n}{1}\cdot{n}{2}\cdot ... ⋅nk\cdot{n}{k}:

x≡(a1⋅Nn1⋅((Nn1)−1  mod  n1))+(a2⋅Nn2⋅((Nn2)−1  mod  n2))+{x}\equiv{\left({a}_{{1}}\cdot\frac{{N}}{{{n}_{{1}}}}\cdot{\left({\left(\frac{{N}}{{{n}_{{1}}}}\right)}^{{-{1}}}\ \text{ mod }\ {n}_{{1}}\right)}\right)}+{\left({a}_{{2}}\cdot\frac{{N}}{{{n}_{{2}}}}\cdot{\left({\left(\frac{{N}}{{{n}_{{2}}}}\right)}^{{-{1}}}\ \text{ mod }\ {n}_{{2}}\right)}\right)}+ ... +(ak⋅Nnk⋅((Nnk)−1  mod  nk))(mod  N)+{\left({a}_{{k}}\cdot\frac{{N}}{{{n}_{{k}}}}\cdot{\left({\left(\frac{{N}}{{{n}_{{k}}}}\right)}^{{-{1}}}\ \text{ mod }\ {n}_{{k}}\right)}\right)}{\left(\text{mod }\ {N}\right)}

In the context of RSA, we have N=p⋅q{N}={p}\cdot{q} where p{p} and q{q} are distinct prime numbers, and thus, they are coprime.

m ≡ m (mod p)
m ≡ m (mod q)

Example

Based on the systems of congruence from the previous RSA calculation example:

m≡m  mod  p≡42  mod  7≡0  mod  7{m}\equiv{m}\ \text{ mod }\ {p}\equiv{42}\ \text{ mod }\ {7}\equiv{0}\ \text{ mod }\ {7}

m≡med≡m1+k⋅ϕ(q)≡m1⋅(mϕ(q))k≡m⋅1k  mod  q≡42  mod  11{m}\equiv{m}^{{{e}{d}}}\equiv{m}^{{{1}+{k}\cdot\phi{\left({q}\right)}}}\equiv{m}^{{1}}\cdot{\left({m}^{{\phi{\left({q}\right)}}}\right)}^{{k}}\equiv{m}\cdot{1}^{{k}}\ \text{ mod }\ {q}\equiv{42}\ \text{ mod }\ {11}

We now use the CRT step by step:

m=((m  mod  p)⋅p⋅qp⋅((p⋅qp)−1  mod  p))+((m  mod  q)⋅p⋅qq⋅((p⋅qq)−1  mod  p))(mod  p⋅q){m}={\left({\left({m}\ \text{ mod }\ {p}\right)}\cdot\frac{{{p}\cdot{q}}}{{p}}\cdot{\left({\left(\frac{{{p}\cdot{q}}}{{p}}\right)}^{{-{1}}}\ \text{ mod }\ {p}\right)}\right)}+{\left({\left({m}\ \text{ mod }\ {q}\right)}\cdot\frac{{{p}\cdot{q}}}{{q}}\cdot{\left({\left(\frac{{{p}\cdot{q}}}{{q}}\right)}^{{-{1}}}\ \text{ mod }\ {p}\right)}\right)}{\left(\text{mod }\ {p}\cdot{q}\right)}

m=((m  mod  p)⋅q⋅(q−1  mod  p))+((m  mod  q)⋅p⋅(p−1  mod  q))(mod  p⋅q){m}={\left({\left({m}\ \text{ mod }\ {p}\right)}\cdot{q}\cdot{\left({q}^{{-{1}}}\ \text{ mod }\ {p}\right)}\right)}+{\left({\left({m}\ \text{ mod }\ {q}\right)}\cdot{p}\cdot{\left({p}^{{-{1}}}\ \text{ mod }\ {q}\right)}\right)}{\left(\text{mod }\ {p}\cdot{q}\right)}

m=((0  mod  p)⋅11⋅(11−1  mod  7))+((42  mod  q)⋅7⋅(7−1  mod  11))(mod  7⋅11){m}={\left({\left({0}\ \text{ mod }\ {p}\right)}\cdot{11}\cdot{\left({11}^{{-{1}}}\ \text{ mod }\ {7}\right)}\right)}+{\left({\left({42}\ \text{ mod }\ {q}\right)}\cdot{7}\cdot{\left({7}^{{-{1}}}\ \text{ mod }\ {11}\right)}\right)}{\left(\text{mod }\ {7}\cdot{11}\right)}

m=(0⋅11⋅2)+(9⋅7⋅8)(mod  77){m}={\left({0}\cdot{11}\cdot{2}\right)}+{\left({9}\cdot{7}\cdot{8}\right)}{\left(\text{mod }\ {77}\right)}

m=504(mod  77)=42{m}={504}{\left(\text{mod }\ {77}\right)}={42}